 ZIEN
Z-IoTPhysical AI Product Security
Physical AI
firmware testing solution
Automatically finds vulnerabilities in Physical AI firmware
From default passwords to certificates and crypto keys, binaries, SBOMs and zero-days. No IoT hacking expertise needed — upload your firmware and it's tested automatically.
For · Physical AI and appliance manufacturers · companies pursuing overseas certification (RED, CRA)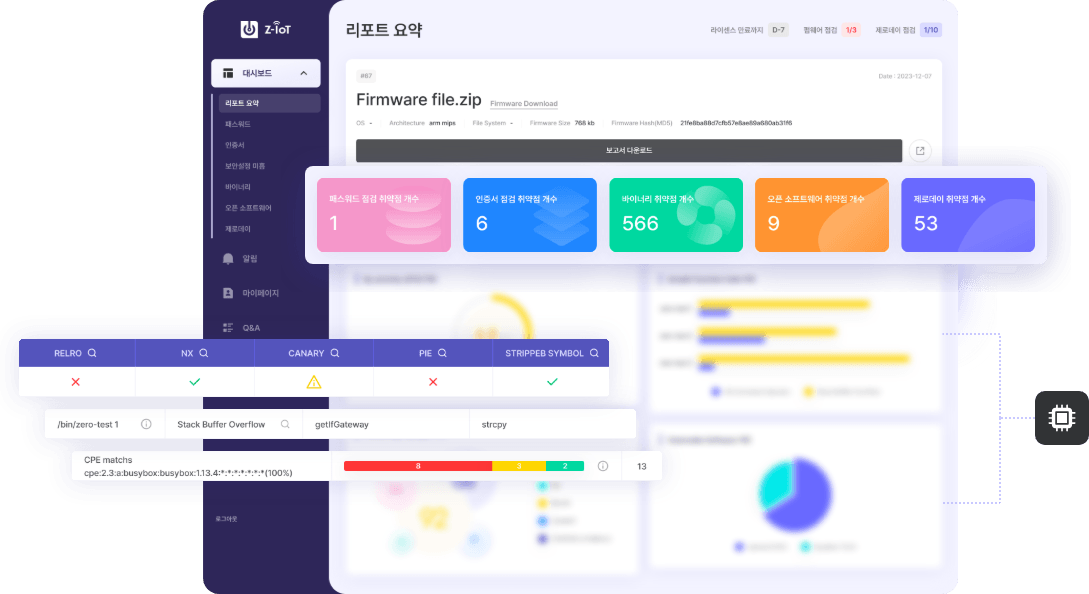
WHY FIRMWAREIf you build Physical AI products,
If you build Physical AI products,
regular firmware hacking is a must
No product is tested once and done. Every time the firmware changes, it has to be attacked again.
WHAT WE DO
Years of tearing down real devices, built into the analysis engine
ZIEN has opened up real devices — wall pads, robot vacuums, in-vehicle infotainment systems — pulled out their firmware and attacked it. We've turned those analysis methods into five engines, so testing that experts once did by hand now runs automatically.
WHY Z-IoT01“Could our products have them too?” 02“Will a tool really find them?” 03“Can we trust the results?” 04“Can a small manufacturer like us use it?”
Even certified products have vulnerabilities
Here are our answers, in order, to the four questions product security and certification teams ask before adopting.
67 CVEs and KVEs we found ourselves — the same methods, built in
The engine carries the analysis methods ZIEN's research team has used to uncover zero-days.Officially used in a study by the Korea Consumer Agency and the Korea Internet & Security Agency (KISA)
Used as the testing tool in a 2025 security study of robot vacuums sold in Korea.Annual security assessment campaign for SME manufacturers with KEA
Every year, together with the Korea Electronics Association (KEA), we use Z-IoT to assess and strengthen the security of SME manufacturers' products.SCOPE
Three things you get from one firmware file
Upload a single firmware file and get one report covering vulnerabilities, how to fix them and where you stand on compliance.
01
Vulnerability discovery
Five analysis engines automatically find the vulnerabilities in your firmware.02
AI patch guide
For each vulnerability found, AI summarizes the cause and the fix so developers can act on it right away.03
Compliance status
Test results are automatically mapped to regulatory requirements such as EN 18031, EN 303 645 and NIST IR, showing whether each one is met.USE CASESIoT manufacturers
How is it used?
As a security tool during development
Upload firmware with every build to catch vulnerabilities before release. The same report prepares the SBOM and compliance status you need for certification audits.DevelopBuildZ-IoT scanRelease
WORKS WITH
Firmware is tested automatically; hardware and penetration testing by experts
Z-IoT tests firmware automatically, while ZIEN's experts carry out the hardware analysis and penetration testing that tools can't handle.
Z-IoT · Automated
Firmware testing
- Passwords · certificates · binaries · open source · zero-days
- Five analysis engines run automatically
ZIEN experts · Hands-on
Hardware analysis · penetration testing
- Hardware analysis that opens up the real device
- Penetration testing with real attack scenarios
Security roadmaps by industry
CONTACT
Talk to us about adopting Z-IoT
Tell us about your environment and the product lines you want analyzed, and we'll reply within 5 business days with deployment options and a demo schedule.
support@zi-en.io · +82-70-4571-9854FAQ
Frequently asked questions
QWhat does it test?View details ▾
It automatically tests five areas from a single firmware file.
01Credentials · certificates02Binaries · open source03Zero-days
QWhich devices and architectures are supported?View details ▾
We support Linux- and Android-based IoT firmware.
01Smart home · city · factory02Medical · autonomous driving03Linux · Android
QHow do we adopt it?View details ▾
Choose between a cloud subscription (SaaS) and an in-house deployment (on-premises). Contact us for pricing.
01SaaS subscription · monthly or annual plans, for SMBs and smaller organizations02On-premises · licensed, deployed in-house at manufacturers03Contact us
Related reading
 IoT regulation
Global IoT Security Regulations & Certification Landscape: How Z-IoT Helps You Stay Compliant with Evolving Global Standards ↗
2025.05.22 · ZIEN Lens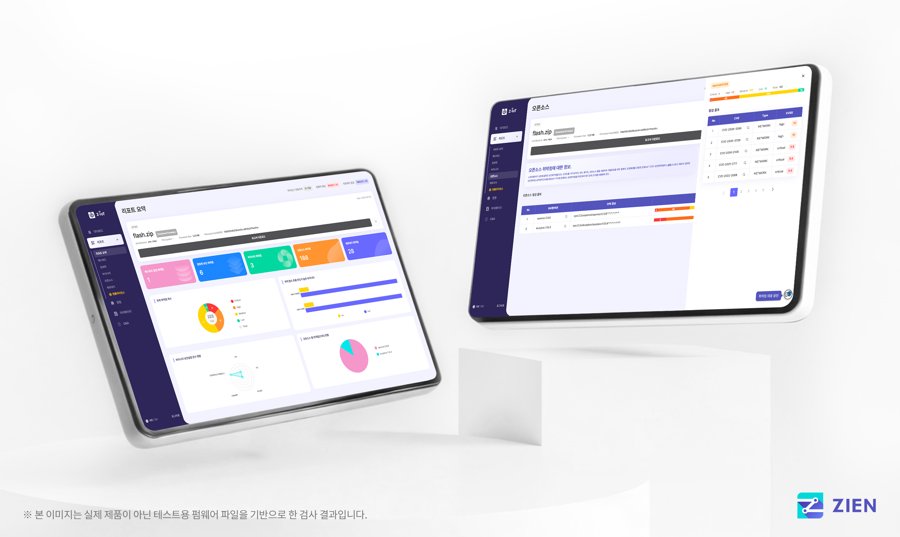 Newsroom
Z-IoT officially used in the KISA and Korea Consumer Agency robot vacuum study
2025.11.19 · BoanNewsNewsroom