Real-world attacks, just as hackers run them — ZIEN's offensive experts try to break in themselves
ZIEN's offensive research team, proven at hacking competitions, breaks into your service following the same steps as a real attacker.
Web
01
WebWe confirm which paths in your web service can actually be breached — login, permissions, input handling and more.
Mobile
02
Android · iOSWe test app tampering, stored data and server communication from an attacker's point of view.
API
03
REST · IntegrationsWe find API issues such as authentication bypass, privilege abuse and excessive data exposure.
Infra
04
Servers · NetworksWe check servers and internal traffic for privilege escalation and lateral movement.
Cloud
05
AWS · Azure · GCPWe test the risks that come from cloud configuration, such as account and permission settings and exposed storage.
Hardware
06
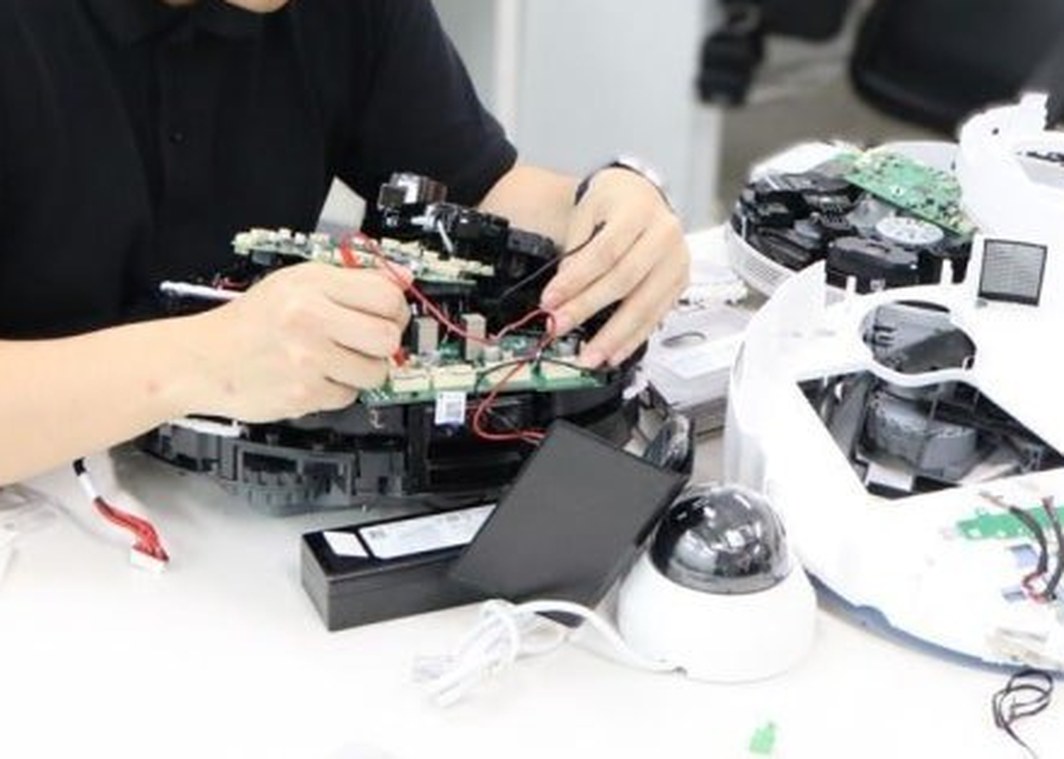
UART · JTAG · ChipsWe open the device and check whether debug ports and memory chips can give us admin access.
Firmware
07
Dump · Analyze · TamperWe extract the firmware and check it for hard-coded keys and accounts, vulnerable components and tampering potential.
Wireless
08
Wi-Fi · BLE · ZigbeeWe check whether wireless traffic can be intercepted, or the device controlled with spoofed signals.
Internal network
09
AD · PivotingOnce inside the corporate network, we follow how far we can get — all the way to core servers and accounts.
AI & LLM
10
Prompt injectionWe test whether manipulated prompts can bypass instructions or pull out internal data.
WHO DOES IT
A team proven on stage does the testing itself
From government competition awards to Pwn2Own, the world's top hacking competition, ZIEN's offensive research team — proven on real products — carries out every test itself.
2
Consecutive years of Pwn2Own exploits
100+
Zero-day vulnerabilities discovered
10
Patents (Korea · US)
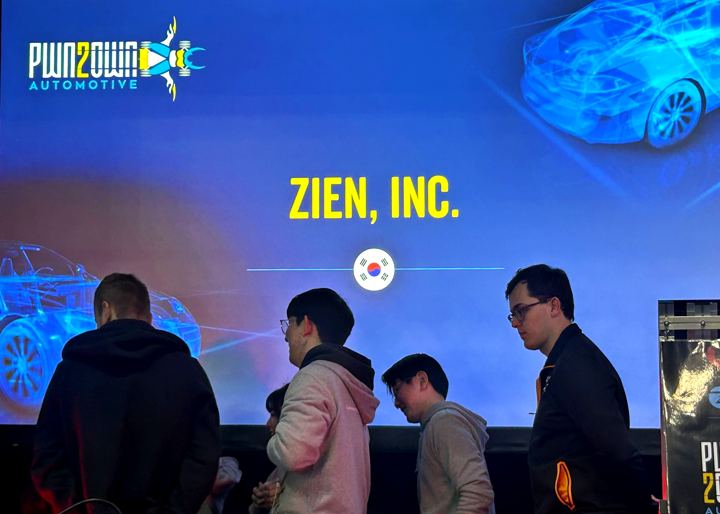
Jan 2026Pwn2Own Automotive 2026Successful exploitSuccessfully hacked an EV charger
2025Pwn2Own Automotive 2025Successful exploitSuccessfully hacked an in-vehicle infotainment system
Aug 2024DEF CON 32 · Hack the TVWinnerWon the TV hacking CTF
Oct 2023IITP President's AwardAwardCyber Security Challenge (smart city security)
Dec 2022Minister of Science and ICT Award1st placeCyber Security Challenge (smart home security)
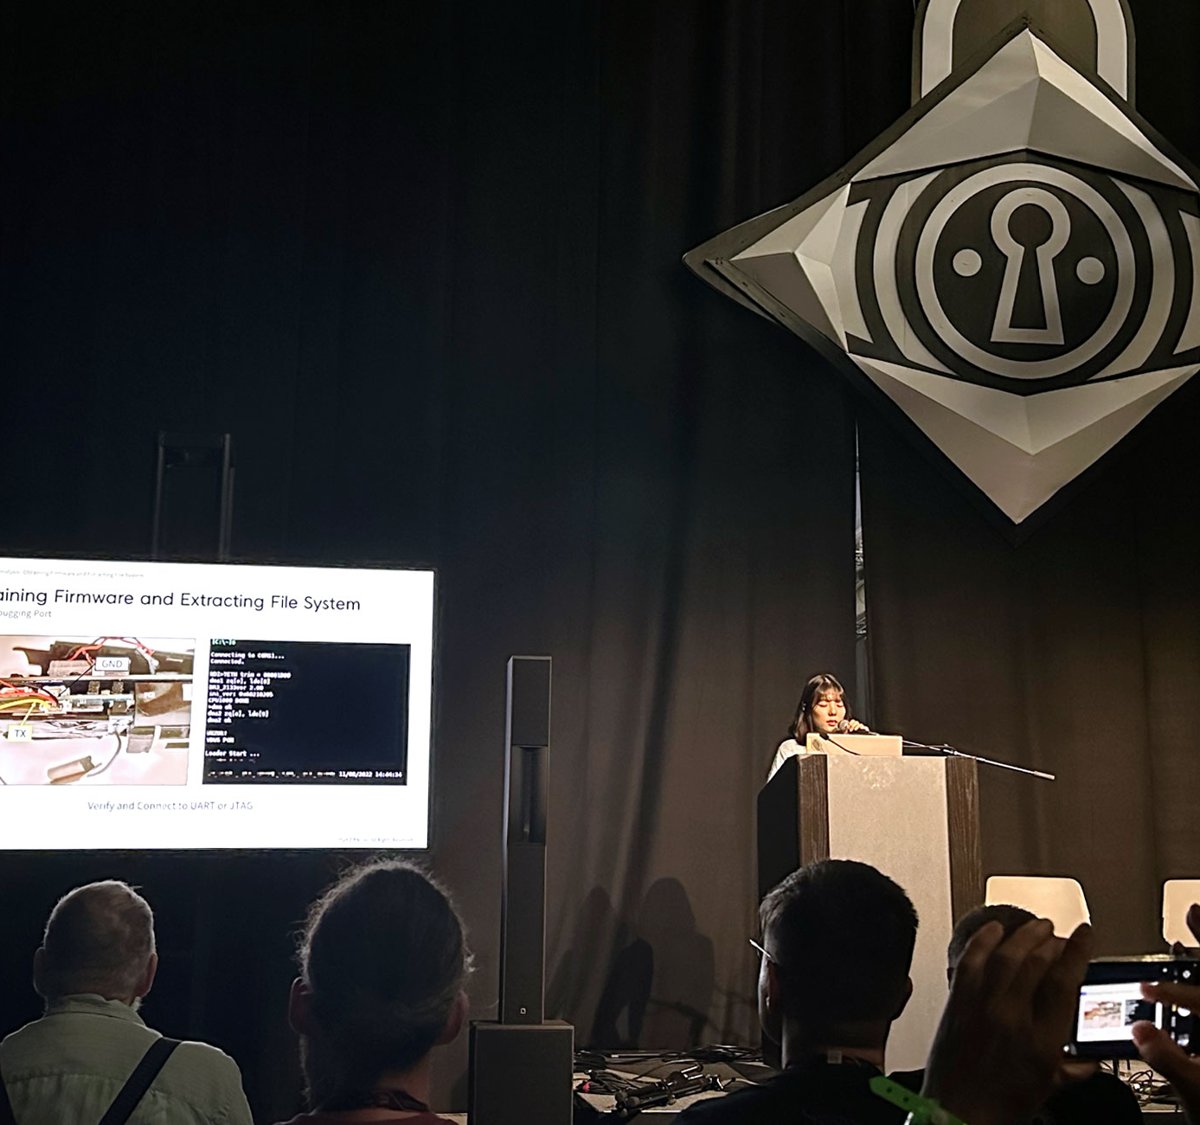
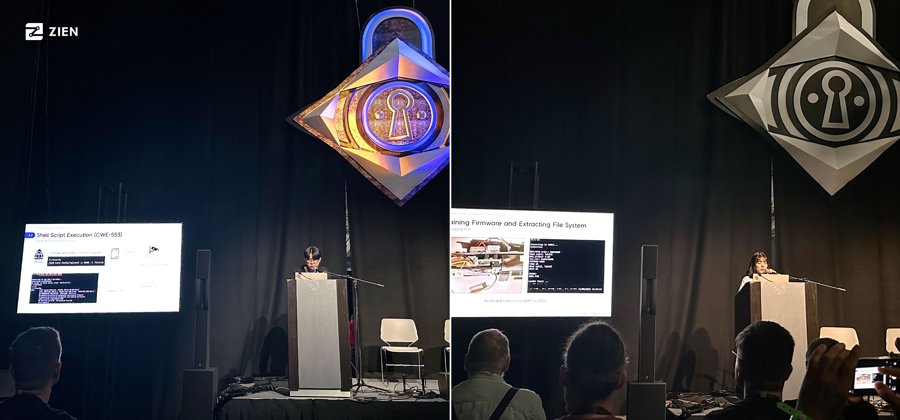
Presenting at DEF CON · Firmware extraction demo
CONTACT
Just tell us what to test
Tell us what you'd like tested, and we'll reply within 5 business days with a proposed scope and timeline.
support@zi-en.io · +82-70-4571-9854
FAQ
Frequently asked questions
QWhat do you test?View details ▾
From web, mobile and APIs to cloud and internal networks, we look at every path a real attacker could use to get in.
01Web & mobile02Cloud03Servers & networks
QHow is this different from an automated vulnerability scanner?View details ▾
Scanners stop at finding known patterns. ZIEN chains multiple vulnerabilities the way an attacker would to see how far a breach can really go — and reports only what is actually dangerous.
QHow much information do we need to provide?View details ▾
We can start with no information at all, like an outside attacker, or take accounts and design documents to go deeper. We'll choose the approach together based on your goals.
01Black box02Gray box03White box
QHow long does it take, and will it affect operations?View details ▾
It depends on the scope. We agree on time windows and intensity in advance so testing doesn't disrupt your operations.
01Agreed timeline02Set time windows03Controlled intensity
QWhat will we receive?View details ▾
You'll receive a report with reproduction steps and priorities, remediation guidance, and retest results.
01Test report02Remediation guide03Retest results
QHow do we fix the vulnerabilities you find?View details ▾
Fix them by following the report's remediation guide, and track progress by owner and deadline in Z-ONE. Once fixed, we run the same attack again to confirm it's blocked.
01Remediation guide02Managed in Z-ONE03Retest
QCan we get tested on a regular basis?View details ▾
Yes. Every change to your service can introduce new vulnerabilities, so periodic testing on an annual plan is also available.
 ZIEN
 R&D
 Pwn2Own
 Newsroom