 ZIEN
01 · Real hackers attack
Z-ONEHacking assessments for companies without a red team
Worried about hackers?
Leave it to ZIEN
No need to hire a red team — we hack your systems the way one would
Z-ONE is a hacking assessment platform: ZIEN's red team attacks like real hackers, and AI repeats those attacks to confirm the results.
Just tell us what to protect. We'll show you where we got in and how to fix it, in plain language.
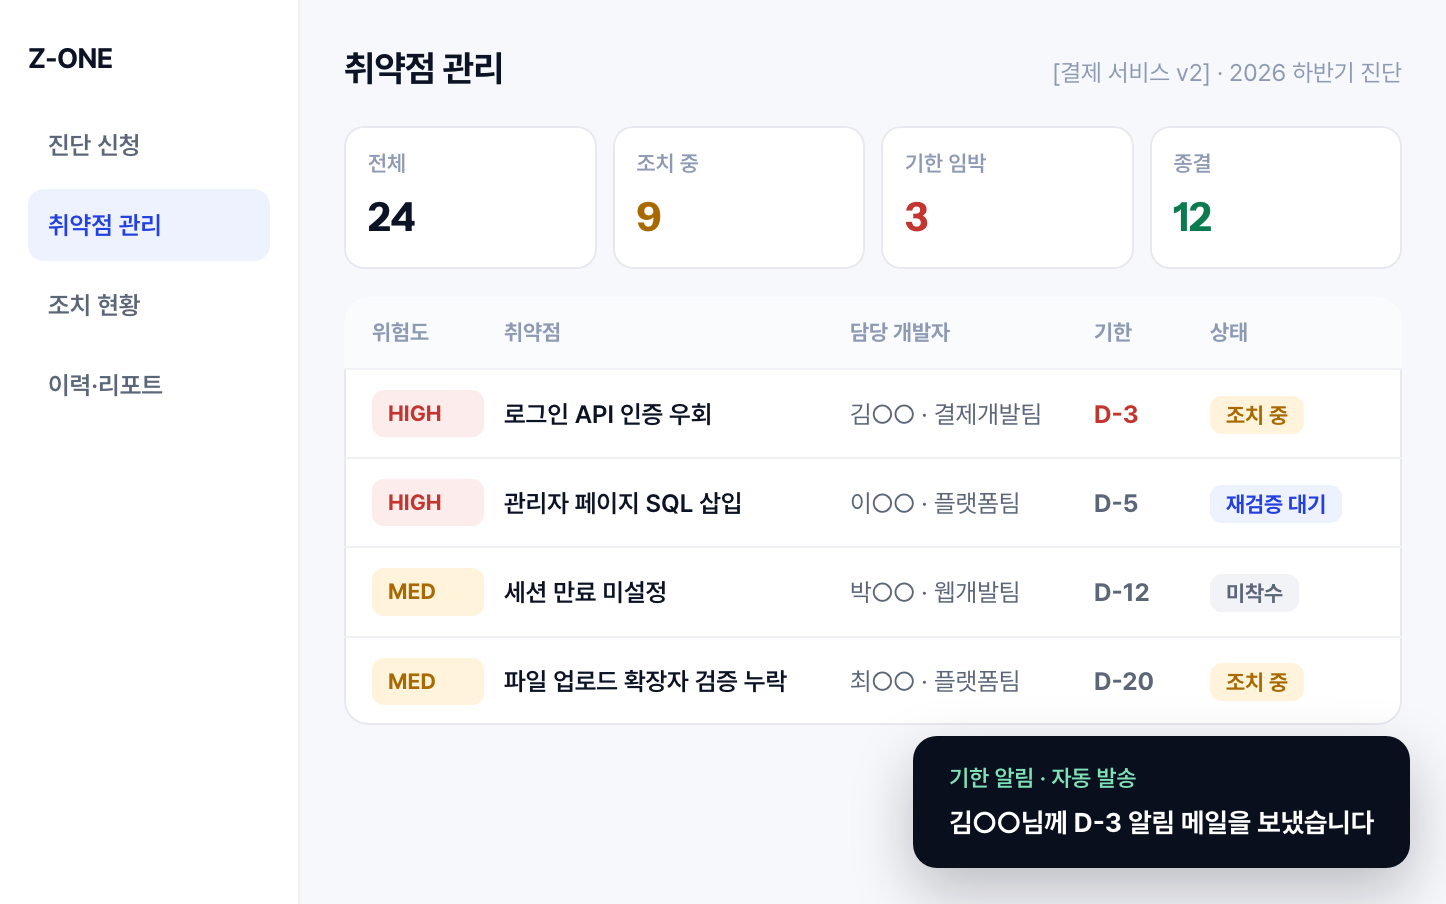
Email alert · Just now3 days left to fixLogin API authentication bypass · Owner: Kim ○○
WHY Z-ONEIf hacking worries you,
If hacking worries you,
break in before the hackers do.
No separate red team needed — ZIEN's red team and AI attack your services for you.
RED TEAM EFFECTYou don't have to hire a red team
You don't have to hire a red team
to have one
Not sure how to approach hacking? That's fine. ZIEN does the attacking, and AI does the repeating.
We break in directly,
ZIEN's red team — with successful Pwn2Own exploits and 100+ zero-days to its name — tests your services through an attacker's eyes.02 · AI repeatsBeta · Coming soon
AI re-runs
the attacks we found
AI retries the attacks ZIEN found, the same way, to confirm the fix really holds. No waiting for the red team's schedule.03 · In plain language
We show you where we got in
and how to close it
Instead of security jargon, we explain in plain language — down to fixes your developers can apply right away.See Z-ONE's actual screens
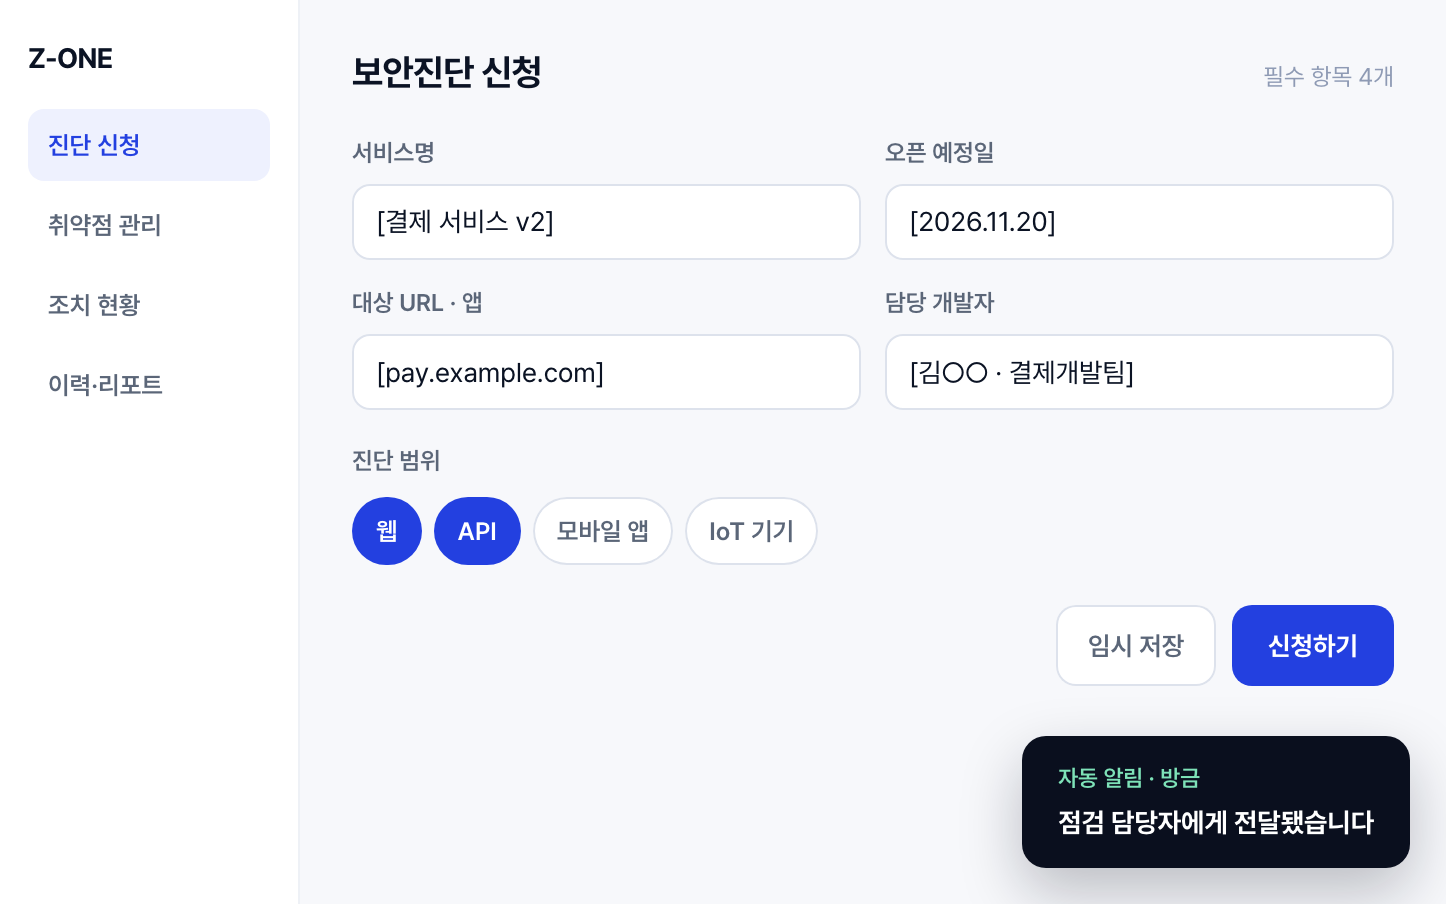
From request to management and history — the screens your team will actually use.
Z-ONE · Request
Z-ONE · Vulnerability management
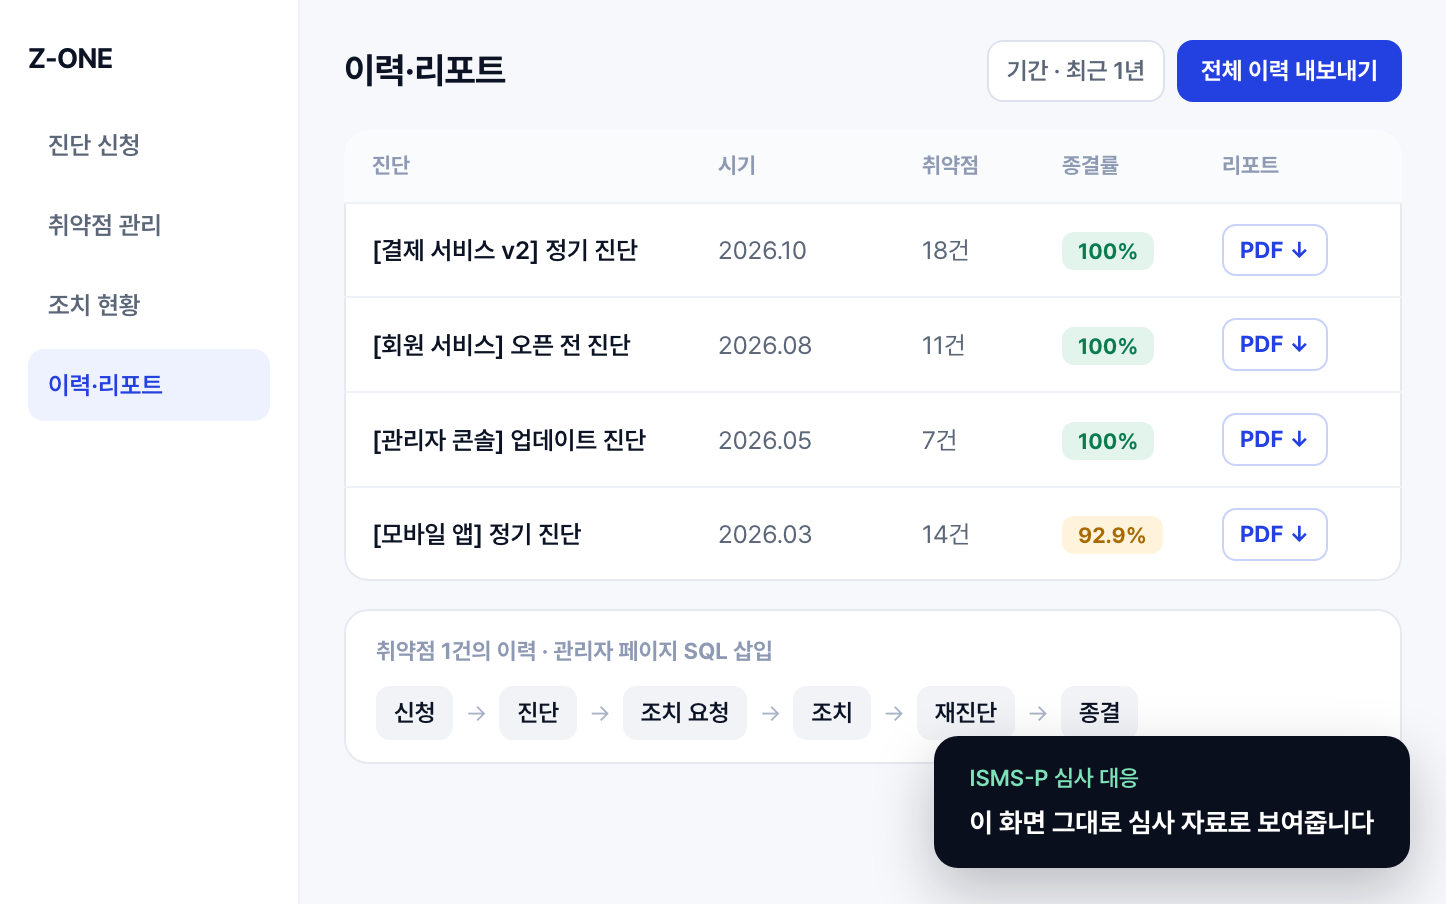
Z-ONE · History & reports
Z-ONE · Retest (beta)
Beta · Coming soonOnce you fix it, AI re-checks it
with the same attackRetesting without waiting on a consultant's schedule. Screens will be unveiled at launch.
with the same attackRetesting without waiting on a consultant's schedule. Screens will be unveiled at launch.
- 1Request a retestDevelopers request it on the platform after fixing
- 2AI retestRe-checked with the same attack ZIEN used in its assessment
- 3Close & recordResults are kept in the history as is
Z-PEN + Z-ONE
Z-PEN does the hacking, Z-ONE takes it from there
Findings carry straight over, and we stay with you until every fix is made and verified.
- 01Z-PENFindings are reported with reproduction steps.
ZIEN's red team breaks in directly
- 02Z-ONEEach vulnerability gets an owner and a deadline and is tracked until it's fixed.
Results flow straight into Z-ONE
- 03AI retest · BetaVerified right away, without waiting for the red team's schedule.
After the fix, AI checks with the same attack
- 04NextYou operate the testing, remediation and retest process you built with ZIEN on your own.
Now your company runs it on Z-ONE
The standard package starts Z-PEN assessments and year-round Z-ONE management together.Learn more about Z-PEN →
Adopting Z-ONE? Start with a consultation
We'll shape the assessment scope, schedule and operating model around your organization. We reply within 5 business days.
support@zi-en.io · +82-70-4571-9854Frequently asked questions
QCan we use it without dedicated security staff?View details ▾
Yes. Just fill out the request form — ZIEN experts handle the testing and explain the results and fixes in plain language. We organize everything so your developers can fix it right away, and we stay with you through the retest.
01Fill out the request form02ZIEN experts run the test03Results explained in plain language
QCan we adopt Z-ONE on its own, without a ZIEN assessment?View details ▾
The standard package starts Z-PEN expert assessments and year-round Z-ONE management together. If you'd like Z-ONE on its own, contact us and we'll get back to you with an option that fits your environment.
QWhen can we start using AI retest (beta)?View details ▾
You can join the beta test starting January 2027. If you'd like to try it early, pre-register now.
Pre-register for the beta →
Related reading
 PHP2Shell
 — “It Won’t Work in the Real World”? It Worked on Our Server ↗
2026.11.02 · ZIEN Lens React2Shell
 Part 3: After React2Shell, How Should Companies Rebuild Their Response Framework? ↗
2025.12.14 · ZIEN Lens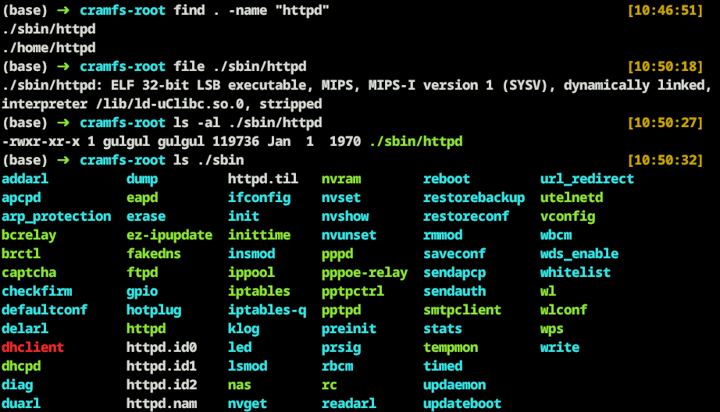 1-day analysis